Artificial intelligence is transforming how enterprises operate. From AI-powered copilots and large language models (LLMs) to autonomous agents connected to business applications, organizations are moving beyond AI experimentation toward systems that can retrieve information, interact with enterprise tools, and execute tasks. But as AI becomes more capable, the security challenge becomes more complex.
An AI agent may appear to be a simple assistant on the surface. Behind the scenes, it could operate through delegated identities, access sensitive business data, invoke APIs, interact with third-party tools, and cross trust boundaries that security teams cannot easily see. If one of these connections is compromised or misused, the consequences may extend far beyond the original AI application.
This is the enterprise AI security challenge Grafyn is built to address: understanding what AI can reach, which identities it uses, what it trusts, and how far risk can spread.
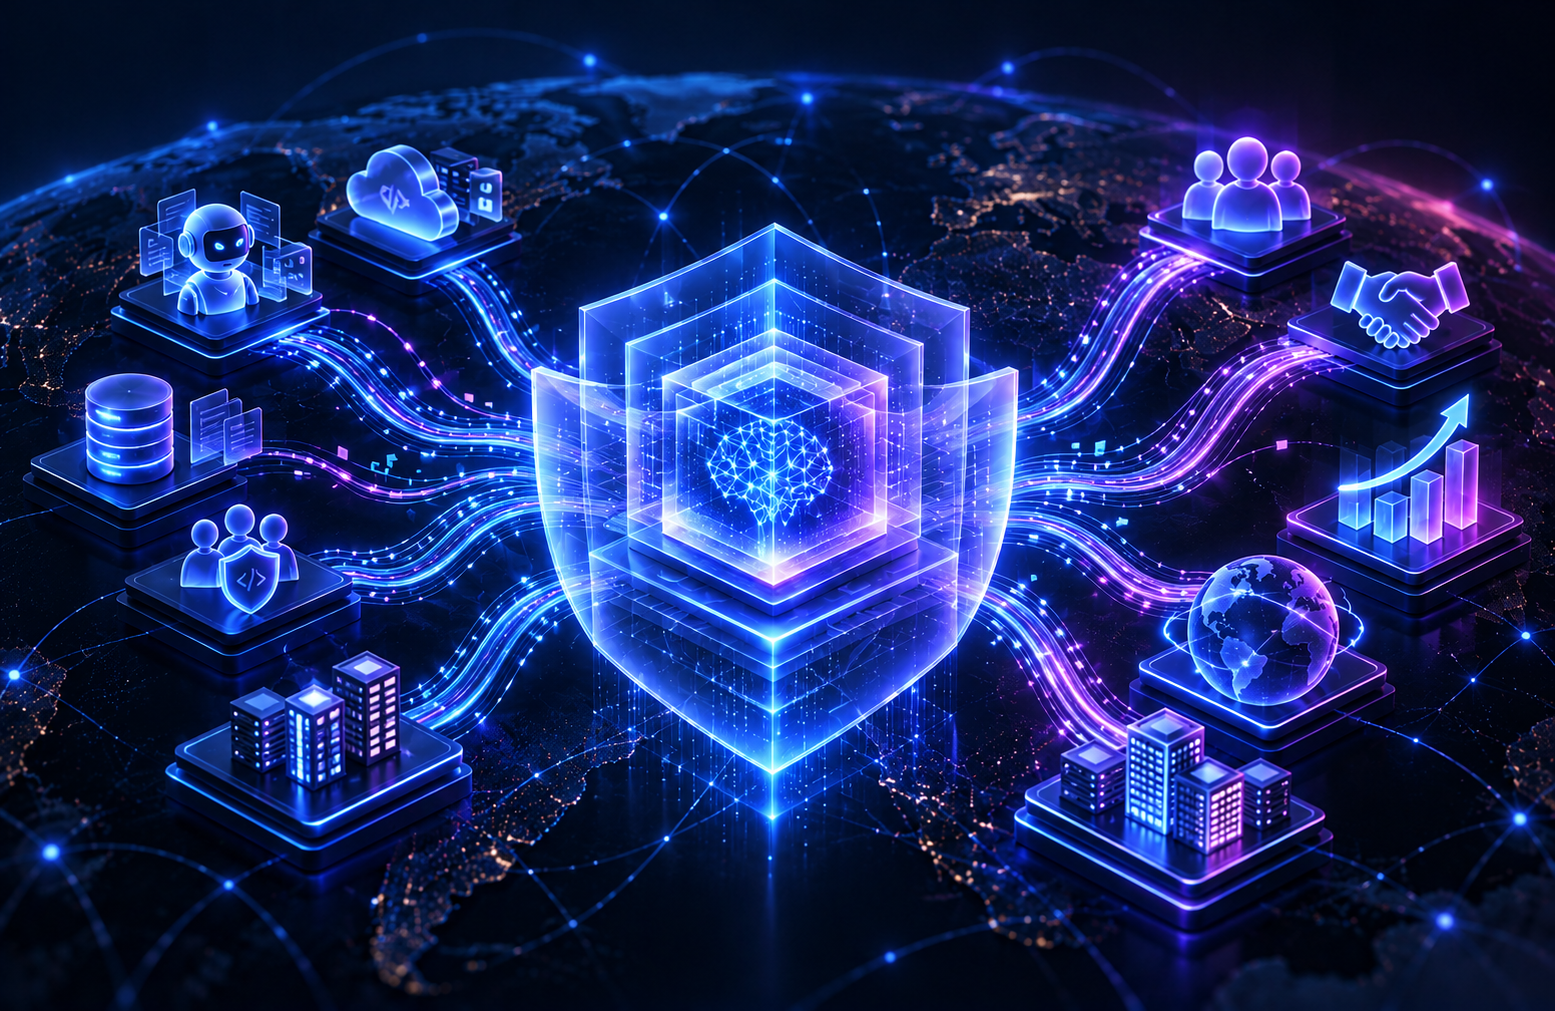
Grafyn helps enterprises discover their AI ecosystem, understand hidden relationships between AI agents and connected systems, assess potential exposure, and reduce their AI security blast radius.
What Is AI Security?
AI security is the practice of identifying, understanding, and reducing security risks associated with AI models, applications, agents, identities, data, tools, and connected enterprise systems.
Traditional cybersecurity protects networks, applications, infrastructure, identities, and information. Enterprise AI security builds on those foundations by addressing the additional complexity created when AI systems retrieve data, inherit permissions, make decisions, invoke tools, and take actions across multiple environments.
For enterprises, the challenge is no longer limited to determining whether an AI application is secure. Security teams must also understand its connections and capabilities.
For example, an AI agent might:
- Retrieve information from internal knowledge repositories.
- Use delegated credentials to access enterprise applications.
- Connect to databases, APIs, and Model Context Protocol (MCP) servers.
- Process sensitive customer or employee information.
- Invoke tools that trigger actions in downstream systems.
Each connection introduces questions about identity, access, data exposure, trust, and potential business impact.
Grafyn approaches enterprise AI security through these interconnected relationships. Rather than examining AI assets in isolation, its platform helps organizations understand the broader environment in which those assets operate.
Why Is AI Security Important for Enterprises?
AI adoption is expanding across enterprise applications, cloud platforms, and business workflows. From AI copilots and coding assistants to autonomous agents, organizations are connecting AI with sensitive data, identities, APIs, and business-critical systems.
These connections create new security challenges. A single AI agent may access multiple applications, inherit delegated permissions, and cross trust boundaries, increasing the potential impact of a security incident.
Without proper visibility, enterprises may struggle to identify Shadow AI, track agent permissions, detect sensitive data exposure, and understand how far a compromise could spread.
Grafyn helps enterprises discover their AI ecosystem, map identity and data relationships, identify hidden exposures, and reduce their AI blast radius to scale AI adoption with greater confidence and control.
What Are the Biggest AI Security Risks for Enterprises?
AI security risks become particularly important when agents connect to business-critical systems. Grafyn focuses on understanding the relationships that can turn an isolated weakness into a wider enterprise incident.
1. Shadow AI and Agent Sprawl
Shadow AI refers to AI applications, agents, tools, and integrations that operate without sufficient organizational visibility or governance.
An employee might introduce an AI assistant into a workflow. A developer might connect an agent to an internal repository. Another team might deploy an MCP server or integrate an external AI service without a complete security assessment. Individually, these decisions may appear manageable. Collectively, they can create an environment that is difficult to inventory and control.
The challenge extends beyond discovering which AI products are being used. Enterprises also need to understand what those tools connect to, which identities they use, and what information they can reach.
Grafyn's discovery and assessment capabilities help organizations identify AI assets, agents, MCPs, tools, and Shadow AI across their environments. This creates a more unified view of the AI ecosystem and helps security teams investigate previously hidden connections
Read more - Shadow AI 2.0: Governing the Invisible Architecture
2. Expanding Identity Chains and Excessive Permissions
AI agents often operate through identities, credentials, roles, API keys, and delegated permissions. An agent may access one application using an authorized identity and then interact with other systems through connected tools. As these relationships expand, its effective access may extend beyond what the original use case requires.
Consider an agent designed to summarize customer records. It might have legitimate access to a CRM system. However, if its identity or connected integrations also provide access to unrelated systems, the agent's potential impact increases. The important question is not just whether the agent has permission to access a particular application. It is how its permissions combine across the entire identity chain.
Grafyn maps identity chains, delegated credentials, and privilege relationships to help enterprises understand who or what an agent acts as, where access may expand, and which exposure paths require attention. This visibility supports more informed access reviews and helps organizations reduce unnecessary reach.
3. Sensitive Data Exposure Across AI Workflows
AI agents can retrieve and process information from multiple sources, including enterprise documents, customer databases, code repositories, data warehouses, and cloud storage. When an agent connects these resources into a single workflow, sensitive information may move across boundaries that security teams do not fully understand.
For example, an agent might retrieve internal information from a knowledge repository and pass it to another connected tool. Assessing the risk requires visibility into the data involved, the systems through which it travels, and the agent's permissions.
A list of AI applications alone cannot reveal these relationships.
Grafyn helps organizations identify sensitive data access and understand potential exposure across agent chains. By mapping data relationships alongside identities and trust boundaries, the platform helps security teams assess where information could be exposed and prioritize the paths that matter most.
4. Trust-Boundary Crossings
Enterprise environments contain multiple trust boundaries, including those between internal applications, external services, cloud environments, databases, and third-party tools. AI agents can operate across these boundaries as part of a single workflow.
The security concern arises when an agent's effective reach extends beyond its intended environment or authority. A connection that appears legitimate in isolation may create a broader risk when combined with other permissions and integrations. This makes trust-boundary analysis an important part of enterprise AI security.
Grafyn identifies where AI agents cross trust boundaries and understand how far their reach extends. This gives security teams additional context for evaluating whether an agent's access and connections align with its intended role.
5. Vector Database (VectorDB) Poisoning and AI Manipulation
VectorDB poisoning is an AI security risk in which malicious or manipulated information is introduced into a vector database, potentially influencing the responses generated by AI systems that rely on retrieval-augmented generation (RAG). For example, an AI agent retrieving information from a compromised vector database could receive misleading or manipulated context that affects its responses, decisions, or downstream actions.
The potential impact depends on the integrity of the retrieved information, the agent's design, permissions, safeguards, and available actions. An agent relying on poisoned knowledge for informational responses may present different risks from one that can access sensitive records and execute actions across enterprise systems. This is why AI security assessments need to consider both the poisoning scenario and the agent's effective reach.
Grafyn's platform includes RAG pipeline poisoning analysis and agent red teaming capabilities designed to help organizations examine potential attack paths and evaluate how far risk could spread. These capabilities complement the broader visibility Grafyn provides into trusted knowledge, identities, data exposure, and trust boundaries.
6. AI Integration and Eco-system Risks
Enterprise AI environments rarely depend on a single model or application. They may combine foundation models, agent frameworks, vector databases, open-source repositories, APIs, cloud platforms, MCP servers, and third-party tools. Every integration adds another relationship that may need to be understood and governed.
A security team evaluating one AI application may not have a complete picture of the systems and identities supporting its operation.
Grafyn is designed to provide vendor-neutral visibility across the broader AI ecosystem, including AI platforms, models, agent frameworks, identities, connected tools, and data stores. This helps enterprises assess risk across their existing environments rather than relying on isolated views of individual AI products.
What Is AI Blast Radius and Why Does It Matter?
AI blast radius is the potential reach of an AI-related security incident: the identities, data, systems, tools, and business processes that could be affected if an AI agent, identity, or connected component were compromised or misused. It is one of the central concepts behind Grafyn's approach to enterprise AI security.
Consider an AI agent that can access a customer database. That access alone represents only part of the security picture. The agent may also use a delegated identity, retrieve information from additional repositories, invoke APIs, or pass data to other connected applications. Each relationship can extend the potential impact of a security failure.
The resulting blast radius depends on the combined reach of the agent and its connections, not merely on the application where it was first deployed.
Grafyn's approach examines three interconnected dimensions:
Identity chain - Who does the AI act as?
Understand the identities, credentials, roles, and delegated permissions through which an agent operates.
Data exposure - What can the AI reach?
Identify the sensitive information and data sources available across an agent's connections.
Trust boundaries - How far can the AI go?
Understand which systems and environments the agent can reach and where its effective authority may extend beyond the intended boundary.
Together, these dimensions help organizations move from simply knowing that an AI agent exists to understanding its potential impact.
The goal is not to eliminate every AI connection. It is to identify unnecessary exposure, prioritize the most consequential risks, and reduce the reach of a potential incident.
How Does Grafyn's AI Security Platform Work?
Grafyn's AI Security Platform is built around a practical sequence: discover the AI ecosystem, understand its relationships, measure potential blast radius, and reduce risk.
Step 1: Discover and Assess the AI Ecosystem
Before enterprises can govern AI effectively, they need visibility into what exists.
Grafyn helps discover AI assets, agents, MCPs, tools, and Shadow AI across the environment. Its approach brings these assets into a more unified view so security teams can assess their presence and connections.
This discovery spans the broader AI environment, including AI-enabled endpoints, enterprise platforms, agent frameworks, identities, integrations, and data stores.
The result is a foundation for understanding AI usage beyond the applications already known to security teams.
Step 2: Map Identity, Data, and Trust Relationships
Discovering an agent is only the beginning. Security teams also need to understand how it operates.
Grafyn maps relationships involving delegated identities, credentials, permissions, data access, and trust boundaries. These relationships provide context about the agent's effective reach.
For example, a security team can investigate which identity an agent uses, which resources it can access, and which connected systems could be affected by a particular exposure. This relationship-based view helps reveal risks that may be difficult to identify by evaluating each application independently.
Step 3: Measure AI Blast Radius
Once the environment and its relationships are understood, organizations can assess how far a potential security incident could spread.
Grafyn's blast-radius analysis helps security teams examine the potential reach of a compromised agent, identity, or tool across connected systems.
Instead of treating every AI asset as an isolated risk, teams can investigate the wider paths through which exposure may travel. This helps provide context for prioritizing remediation based on potential business and operational impact.
Step 4: Analyze, Simulate, and Reduce Exposure
Grafyn's platform includes attack simulation and agent red teaming capabilities to help organizations examine potential attack paths and assess whether risks can be contained.
The platform also supports prioritizing exposures, containing unnecessary reach, and strengthening preventive controls.
This connects discovery with practical risk reduction: identify the assets, understand the relationships, investigate potential attack paths, and take action to reduce the blast radius.
Read more - Agentic AI Red Teaming: The Playbook for Building Safe Autonomous AI
AI Security Best Practices for Enterprises
Organizations can strengthen enterprise AI security by applying the following practices alongside a platform that provides visibility into AI assets and their relationships.
1. Maintain a Unified AI Inventory
Identify AI applications, agents, copilots, MCPs, models, tools, and integrations across endpoints, cloud platforms, and development environments. Include unmanaged AI usage wherever it can be discovered.
2. Understand Effective Permissions
Review the identities, delegated credentials, roles, and permissions used by AI agents. Assess the combined access available through connected systems, not just the permissions assigned to an individual application.
3. Map Sensitive Data Access
Determine which sensitive information AI systems can retrieve or process and which downstream tools may receive that information.
4. Identify Trust-Boundary Crossings
Examine connections between internal systems, cloud services, third-party platforms, and external tools. Investigate whether an agent's reach extends beyond its intended authority.
5. Test Potential Attack Paths
Include AI-specific scenarios in security assessments, such as prompt injection, unauthorized tool use, sensitive data exposure, and misuse of delegated permissions. Where appropriate, use attack simulation and agent red teaming to examine potential impact.
6. Prioritize Risks by Potential Impact
Focus on exposures that could affect sensitive data, privileged identities, business-critical applications, or multiple connected systems. Blast-radius analysis can help provide context for prioritization.
7. Establish Continuous Governance
Define policies for AI adoption, permissions, data usage, testing, third-party integrations, and incident response. Reassess the environment as AI systems and their relationships change.
These practices help create a security program that supports responsible AI adoption rather than relying solely on restrictions or disconnected point-in-time reviews.
AI Security vs. Traditional Cybersecurity
AI security and traditional cybersecurity share many foundational controls, but they address different aspects of the enterprise environment.
Traditional cybersecurity focuses on protecting infrastructure, applications, networks, identities, and data. AI security must also account for the behavior and relationships of systems that can retrieve information, use tools, and act through delegated identities.
For enterprise AI, the distinction is especially important because a single agent can connect multiple systems into one operational workflow. A conventional application security review might establish that an application is authorized to access a particular resource. An AI security assessment also needs to examine how that access combines with the agent's other permissions, connections, and potential actions.
Grafyn extends the security perspective from individual AI assets to their interconnected environment. Its emphasis on identity chains, data exposure, trust boundaries, attack simulation, and blast-radius reduction helps organizations evaluate the potential impact of AI-related incidents across the systems they already use.
Why Enterprises Choose Grafyn for AI Security
As AI becomes more deeply integrated into enterprise workflows, organizations need a security approach that can account for the connections between agents, identities, data, and applications.
Grafyn is designed around this challenge.
Visibility across the AI ecosystem: Discover AI agents, tools, MCPs, and Shadow AI across the environment.
Identity-chain mapping: Understand which identities agents use and how delegated credentials and permissions influence their reach.
Data-exposure analysis: Identify sensitive data access and investigate potential exposure across connected systems.
Trust-boundary analysis: Understand where agents cross boundaries and how their effective reach may extend.
Blast-radius analysis: Assess how far an incident involving an agent, identity, or tool could spread.
Agent red teaming and attack simulation: Examine potential attack paths and evaluate risk containment.
Governance and compliance support: Support audit readiness and policy alignment with recognized AI security and risk-management frameworks.
Vendor-neutral coverage: Build visibility across the AI platforms, models, agent frameworks, identities, and data stores already used by the organization.
Together, these capabilities help security teams understand not only where AI exists, but also what it can reach and how its potential impact can be reduced.
The Future of Enterprise AI Security
Enterprise AI is moving toward increasingly connected and autonomous workflows. As organizations introduce more agents and integrate them with additional business systems, the relationships between AI, identity, data, and trust will become increasingly important.
Security teams will need to move beyond asset inventories and isolated application assessments toward a more contextual understanding of risk.
The critical questions will be:
- What can each AI agent access?
- Which identity does it operate through?
- Which systems and data can it reach indirectly?
- Where can its actions cross trust boundaries?
- How far could a compromise spread?
- Which controls can reduce that potential impact?
Grafyn's focus on AI blast-radius reduction addresses these questions by connecting discovery, relationship mapping, exposure analysis, simulation, and governance.
The objective is not to slow AI innovation. It is to help enterprises understand the security implications of their AI ecosystems and make informed decisions about how those systems should operate.
Final Thoughts: Secure Your AI Before Risk Spreads
AI security is becoming a critical requirement as enterprises move from AI experimentation to connected, action-oriented systems. The challenge is not simply protecting models or approving AI applications. It is understanding the relationships that determine what an AI agent can access, which identities it uses, which boundaries it crosses, and how far a security incident could spread.
Grafyn helps enterprises address this challenge through AI discovery, identity-chain mapping, data-exposure analysis, trust-boundary visibility, attack simulation, and blast-radius reduction. By making these relationships visible, Grafyn helps organizations identify hidden exposure, prioritize risks, and strengthen the controls needed to scale AI responsibly.
See what every AI agent in your enterprise can reach. Understand where risk can spread. Take steps to reduce your AI blast radius.
Ready to understand your AI security landscape? Contact Grafyn